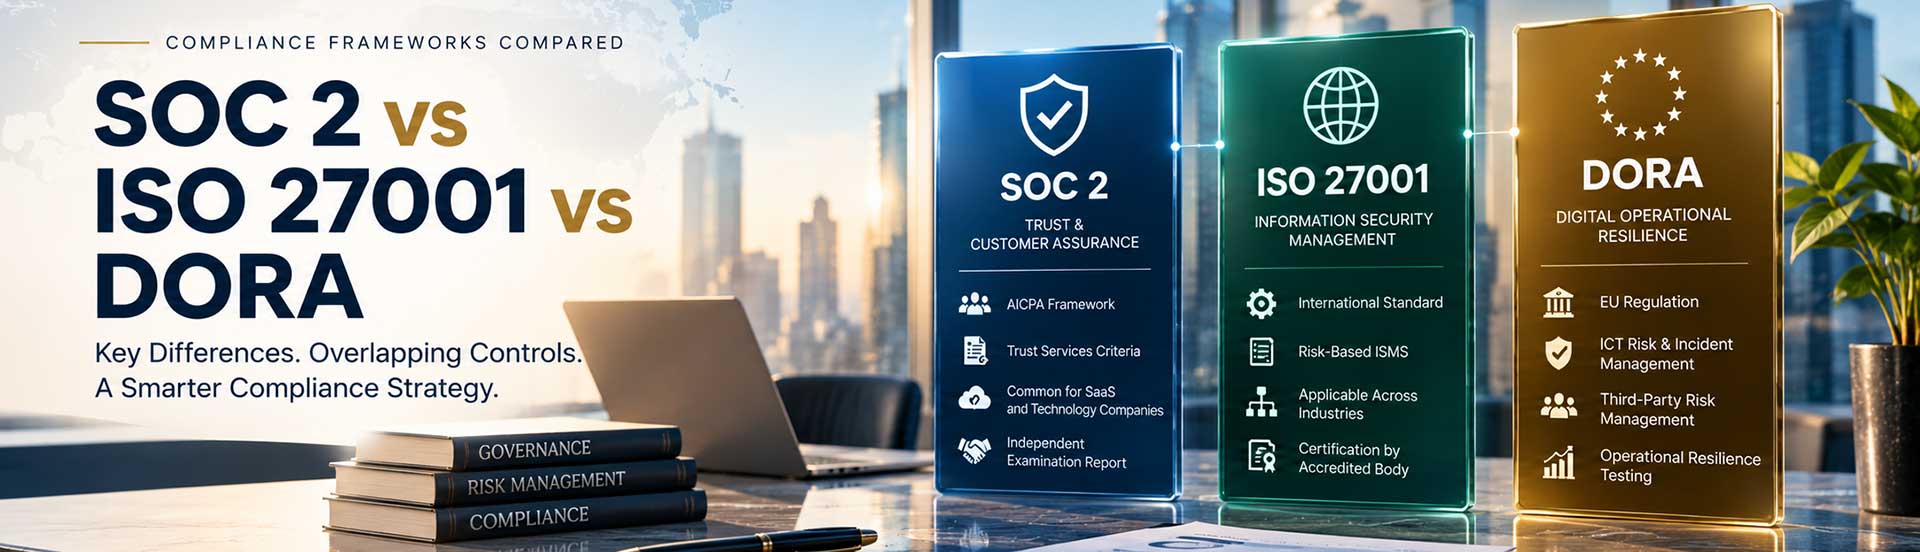
SOC 2 vs. ISO 27001 vs. DORA

SOC 2 vs ISO 27001 vs DORA: How to Choose the Right Compliance Strategy in 2026 Introduction As businesses expand into enterprise markets, security compliance becomes more than a documentation exercise. Customers want assurance that their vendors protect sensitive information, manage cyber risks, and maintain reliable services. Three frameworks frequently come up in these conversations: [...]
2026-10-18T16:45:07+00:00August 18th, 2026|compliance, DORA|

AI security and SOC 2 compliance

AI Security and SOC 2 Compliance: What SaaS Companies Need to Know in 2026 Introduction Artificial intelligence is becoming part of everyday business operations. SaaS companies use AI to automate workflows, analyze customer information, generate content, support development, and improve customer experiences. However, AI adoption also introduces security and governance questions. Where is customer data [...]

2026-10-18T16:47:08+00:00June 24th, 2026|compliance, DORA|

DORA Compliance & Third-Party Risk Management

DORA Compliance in 2026: Why Third-Party Risk Management Is a Business Priority Introduction Financial services depend on an increasingly interconnected technology ecosystem. Banks, payment institutions, fintech companies, and insurance providers rely on cloud platforms, SaaS applications, managed security services, and outsourced infrastructure to deliver critical services. But what happens when a technology provider faces a [...]

2026-10-18T16:35:06+00:00April 18th, 2026|compliance, DORA|
Go to Top